CASOON Open Source
Accessibility audits of the rendered page.
auditmysite loads each page in Chrome, reads Chrome's own accessibility tree over the DevTools Protocol and checks it against WCAG 2.2 AA. One binary, JSON for automation, PDF reports in German and English.
curl -fsSL https://raw.githubusercontent.com/casoon/auditmysite/main/install.sh | bashcargo install auditmysite
$ auditmysite https://www.casoon.de/ \
> --format table --no-sitemap-suggest \
> --lang en --request-mode browser

    _             _ _ _   __  __       ____  _ _
   / \  _   _  __| (_) |_|  \/  |_   _/ ___|(_) |_ ___
  / _ \| | | |/ _` | | __| |\/| | | | \___ \| | __/ _ \
 / ___ \ |_| | (_| | | |_| |  | | |_| |___) | | ||  __/
/_/   \_\__,_|\__,_|_|\__|_|  |_|\__, |____/|_|\__\___|
                                 |___/

  AuditMySite v1.7.0 - WCAG 2.2 AA Accessibility Checker

Checking: https://www.casoon.de/
Auditing: https://www.casoon.de/
✔ Website Health Report

  Accessibility: 100
  Combined technical: 93
  Grade: A
  Certificate: EXCELLENT
  Violations: 0
  Duration: 9561ms

PASS
- WCAG 2.2 A/AA success criteria in scope
- 55
- of them covered by automated checks
- 30
- listed for manual review, never silently passed
- 25
- prebuilt release targets (macOS arm64, Linux x64/arm64, Windows x64)
- 4
What it does
Chrome's accessibility tree, not a static guess
Pages are rendered in Chrome and audited through the DevTools Protocol, so JavaScript-rendered content, computed styles and the browser’s own accessible names are what gets checked.
Honest WCAG coverage
A criterion counts as automated only if a rule can report a violation. The numbers are frozen in docs/PARITY_CONTRACT.jsonc and guarded by a test; every report carries them in summary.wcag_coverage.
JSON contract, PDF for people
The JSON report is canonical English and schema-backed for automation. The PDF is tagged PDF/UA-1 and rendered in English or German (--lang en|de).
Single pages and whole sites
Audit one URL in depth, or a sitemap, a URL list or a same-domain crawl as one aggregated batch report with averages, ranking and recurring issues. Technician mode writes one JSON per page plus a flat findings.jsonl instead.
Shared rules with barrierlab
Common WCAG rules, accessible name computation and HTML conformance come from the barrierlab crates, so the same rule IDs apply in auditmysite, astro-post-audit and liveaudit.
Three ways to a report
The CLI
The Rust binary on this page: a single URL, a sitemap, a URL list or a same-domain crawl, on macOS, Linux and Windows.
AuditMySite Studio
A desktop app (Tauri) on the same audit logic: audits grouped per domain, compared over time, reports written locally as PDF. Alpha, latest release 0.2.13 (21 May 2026). The source is not public; the installers are in the downloads repository.
The report engine
The PDF reports are rendered with renderreport and Typst, as tagged PDF/UA-1. If rendering fails, there is a diagnostic instead of a silent fallback.
Common flags
What to audit
- Sitemap, as one batch report-s<sitemap-url>
- URL list from a file-u<file>
- Same-domain crawl from the URL--crawl
- Cap the number of pages-m<num>
What to check
- Add performance, SEO, security, mobile--full
- WCAG level (AAA is incomplete)-lA|AA|AAA
What to write
- Report format-fjson|pdf|table
- Output file-o<file>
- Report language (default en)--langen|de
- One JSON per page plus findings.jsonl--per-page-reports-fjson
Quickstart
Install the binary, make sure a Chrome is available, point it at a URL. The documentation covers batch modes, reports and CI.
- Install with the installer script,
cargo install auditmysiteor a release binary. - Run
auditmysite browser detect. Without a system Chrome,auditmysite browser installfetches Chrome for Testing. - Run
auditmysite <url>for a report, or-f jsonfor automation.
# check which browser auditmysite will use
auditmysite browser detect

# full single-page audit: a table in the terminal, nothing written
auditmysite https://example.com

# machine-readable, for CI
auditmysite https://example.com -f json -o report.json --quiet

# domain-wide, aggregated
auditmysite --sitemap https://example.com/sitemap.xml --max-pages 20
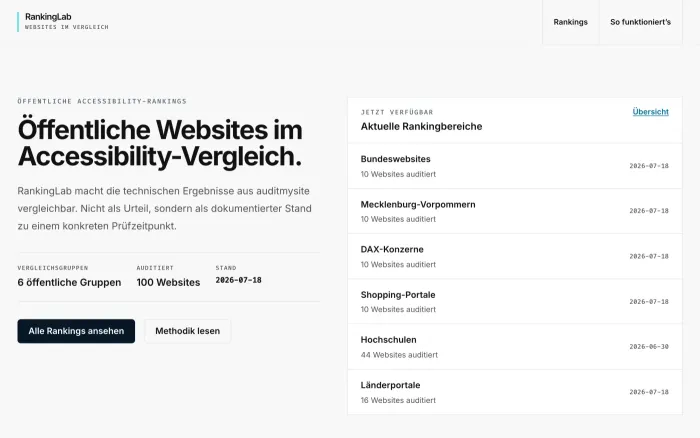
Results from real audits
What an automated audit does not do
Automated checking covers part of accessibility. The rest needs human judgement, and the report says so.
- Not every criterion can be automated
- Keyboard traps, timed content and captions cannot be verified reliably by machine. They are flagged
not_testablein the JSON and listed in the report's audit scope, never silently passed. - No accessibility statement
- The EN 301 549 appendix is a technical building block for a statement written by people. It is not a statement, not legal advice and not a confirmation of conformity under BFSG or BITV 2.0.
- Heuristic modules are tendencies
- Experimental indicators such as UX or AI visibility are off by default; they are estimates, not measurements, and no statement of conformity.
- AAA is not fully implemented
-l AAAexists, but coverage of level AAA is still incomplete.- A browser has to be present
- Without Chrome or Chromium the run stops with an error. A browser is only downloaded on request, with
auditmysite browser install. - Linked PDF documents are not checked
- Rendered web pages are audited. Linked or embedded PDF files are a documented non-goal.
New in v2.0.2
Changelog →- Report: the "legally relevant finding" has one definition for the management card, the screen-reader BFSG callout and each finding's "BFSG-/EAA-Relevanz" row: an open, confirmed finding whose relevance is high or medium (Refs #952-2). The Legal card counts those findings (never fewer than
risk.legal_flags) and is at least "medium" while one is open; the callout says "violations found" only for such a finding or a high-severity screen-reader blocker, low reading-order notes alone read "needs review".risk.legal_flags, the risk score, the verdict and all JSON field names are unchanged:legal_flagsstays the narrower Level-A count, butmanagement_risks[].rationaleand.levelof the Legal card follow the wider set. - Report:
principle_coverage(JSON and PDF) is scoped to the A/AA criteria the "N of ~55 checked automatically" statement counts; criteria that only emit review hints ran but are neither checked nor passed, so the totals (were 40) no longer exceed that statement (30) (Refs #952-5). - Library users: public structs gained fields (
seo::headings::HeadingInfo.hidden,source_quality::SignalValues.total); code that builds them with struct literals must add the fields. - Report: the SEO heading check "Logical hierarchy" fails when the first heading a reader meets is not the H1 ("1 issues, first heading is H2"), like the structure signal and the screen-reader audit; headings hidden from everyone (
hidden,inert,aria-hidden, not rendered) no longer count as first, so casoon.de's closed mega menu no longer makes its H1 "not the first heading" (Refs #952-1). - Report: the 79 touch targets of one finding count as 79 occurrences (scope "Lokal · 79", complexity, project risk "findings affecting 10 or more elements"), not as 1 (Refs #952-3).
- Report: the "Performance & mobile" card lists high-severity findings of those modules and is at least "medium" while one is open, so a good score no longer puts it under strengths next to a high touch-target finding (Refs #952-3).
Frequently asked questions
Does auditmysite download or install a browser automatically?
No. It requires Chrome, Chromium, or a managed browser to already be present and exits with an error if none is found. auditmysite browser install fetches Chrome for Testing, but only when you run it yourself.
Is the PDF report an accessibility statement I can publish?
No. The EN 301 549 appendix and the JSON findings are a technical building block for a statement a person writes; the report explicitly does not claim conformance under BFSG or BITV 2.0.
Does 100% automated pass mean the page is fully WCAG 2.2 AA compliant?
No. Of the 55 WCAG 2.2 A/AA success criteria, only 29 are counted as automated, and a criterion counts there only if a rule can actually report a violation. The other 26 are listed as requiring manual review, never silently marked as passed.
Where do the WCAG rule ids and checks come from?
From the barrierlab crates (a11y-rules, a11y-dom, accname, html-conform, and related crates), a shared Rust monorepo also used by astro-post-audit and LiveAudit, so the same rule id means the same thing across all three tools. Rule ids stay stable across auditmysite releases, with renames documented when a collision is fixed.
Can it audit more than one page at a time?
Yes. Point it at a sitemap, a URL file, or a seed URL with --crawl, and it writes one aggregated batch report with averages, ranking, and recurring issues across pages. --per-page-reports -f json switches that same batch run to one JSON file per page plus a flat findings.jsonl instead.